
Operating System
Cyber threats evolve daily, but these 10 proven cybersecurity tactics can transform your digital defenses. From simple habits to advanced tools, this guide helps safeguard personal data and business systems against modern attacks.
Enable Multi-Factor Authentication Everywhere
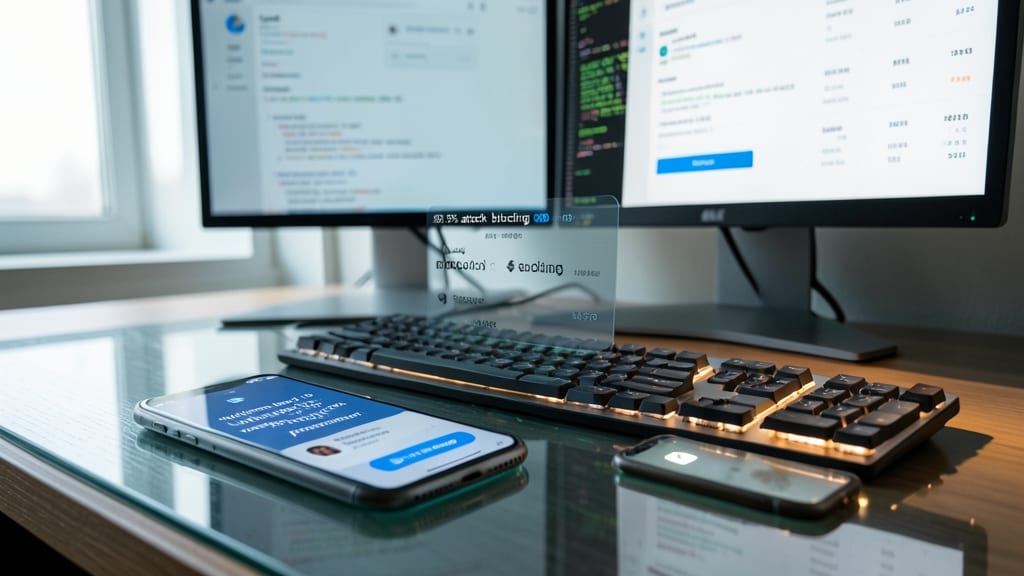
Your email, banking, and social media accounts are prime targets for hackers—but multi-factor authentication (MFA) turns stolen credentials into useless junk. Studies show it blocks 99.9% of automated attacks, making it the single most effective security layer you can add today.
Most platforms now support SMS codes, authenticator apps (like Google Authenticator or Authy), or biometric logins (Face ID/Fingerprint)—all with zero config for most services. Even free options like Microsoft Authenticator or Duo Security (for businesses) offer enterprise-grade protection without complexity. The key? Enable it everywhere: email, cloud storage, and even smart home devices.
This isn’t just for tech experts—small businesses, freelancers, and everyday users all see massive benefits. Start with your most critical accounts, then roll it out systematically. Your future self will thank you. ⚡
Use Password Managers for Secure Storage
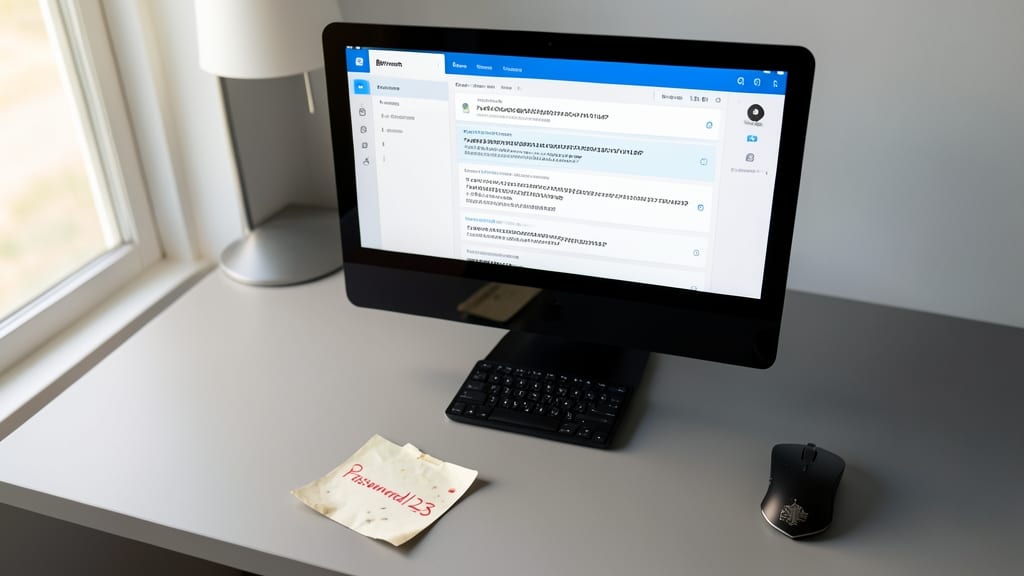
Tired of juggling 50+ passwords that all look like "Password123"? A password manager like Bitwarden or 1Password eliminates guesswork by generating and storing 256-bit encrypted credentials—each with unique, 20-character randomness that even AI crackers can't guess.
These tools auto-fill logins across devices, flag weak passwords, and sync securely via end-to-end encryption. The best (like Bitwarden) even offer open-source verification for transparency. No more sticky notes or browser autofill vulnerabilities—just one master password to remember.
Perfect for freelancers, remote workers, or anyone juggling banking, social media, and work accounts. Your digital life just got a zero-trust vault. ✨
Implement Zero Trust Network Architecture
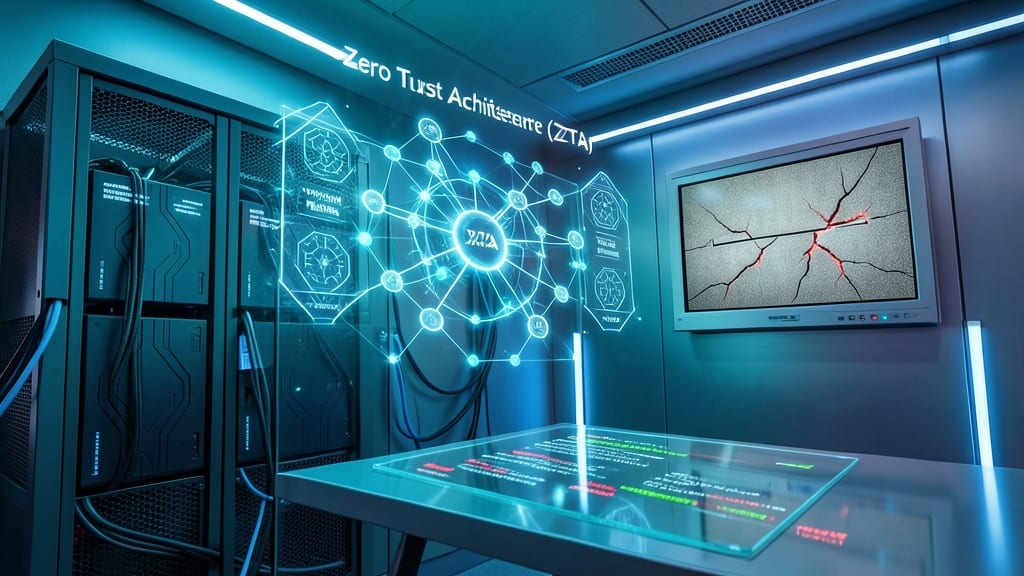
If your business still relies on traditional firewalls as the sole security gatekeeper, you're leaving critical vulnerabilities exposed. Zero Trust Architecture (ZTA) flips the script by assuming breach and verifying every access request—whether from inside or outside your network.
This model requires continuous authentication through tools like Microsoft Azure AD Conditional Access or Okta, where even internal users must re-authenticate for sensitive resources. BeyondCorp by Google takes it further by eliminating VPNs entirely, using context-aware access policies (device health, location, user role) to grant least-privilege permissions. The result? A 70% reduction in lateral movement attacks (Ponemon Institute, 2023) while maintaining productivity.
Ideal for mid-sized enterprises to large corporations handling regulated data (HIPAA, GDPR), ZTA’s modular approach lets you start with identity verification before expanding to micro-segmentation and behavioral analytics. The future of security isn’t perimeter walls—it’s trust no one, verify everything. ✨
Regular Software Updates and Patching
Cybercriminals exploit known vulnerabilities like a buffet—because they’re easy targets. The good news? Regular software updates and patches close 90% of these vulnerabilities before attackers can weaponize them, making it one of the simplest yet most powerful defenses available.
Modern operating systems like Windows 11, macOS Ventura, and Linux distributions now deliver automated, silent updates that patch security flaws within hours of discovery. For IT admins, tools like Windows Update for Business or WSUS let you deploy patches across hundreds of devices with minimal manual effort. Even third-party apps—from browsers to PDF readers—release critical updates that often include zero-day fixes for newly discovered threats.
This isn’t just for tech teams: Home users with smart TVs, routers, or gaming consoles benefit just as much. Set your devices to auto-update where possible, and schedule monthly checks for manual patches. It’s the digital equivalent of locking your doors at night—low effort, high impact. ✨
Deploy Endpoint Detection and Response
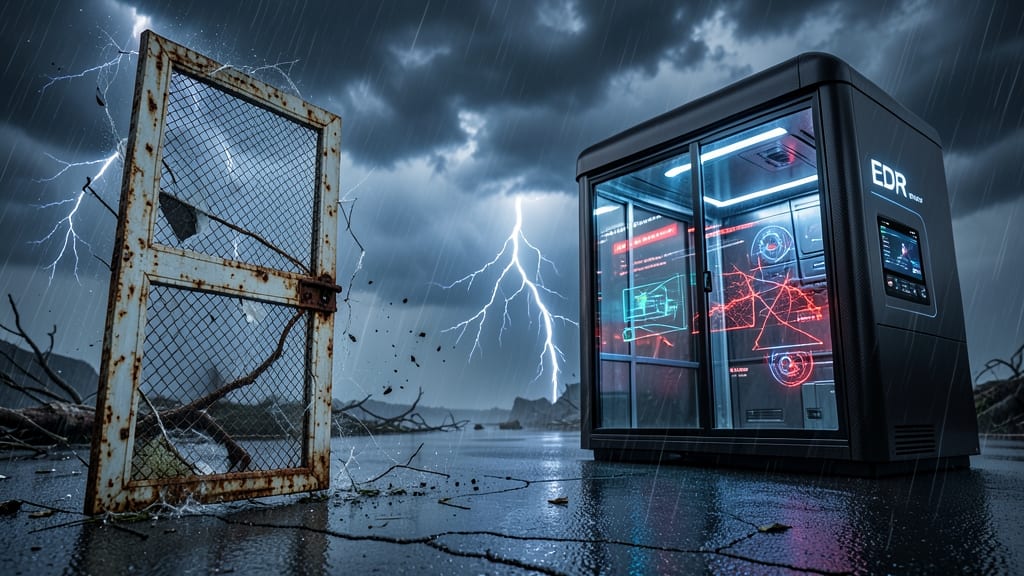
Traditional antivirus solutions are like using a screen door to stop a hurricane—Endpoint Detection and Response (EDR) is the next-gen storm shelter for your devices. While antivirus scans files for known malware signatures, EDR actively hunts for suspicious behavior in real time, stopping advanced threats before they cause damage.
Modern EDR platforms like CrowdStrike or SentinelOne provide AI-driven threat detection, automated response actions, and detailed forensic analysis. They monitor endpoints for anomalies such as unusual process injections, lateral movement attempts, or data exfiltration—red flags that traditional antivirus simply ignores. With sub-second response times, these tools neutralize threats before they spread across your network.
This is non-negotiable for organizations handling sensitive data, but even mid-sized businesses benefit from the visibility into device-level threats. If you’re tired of waiting for the next breach to happen, EDR turns passive defense into proactive threat hunting. ⚡
Educate Employees on Phishing Awareness
Your employees might be your biggest cybersecurity risk—and that’s not a criticism, it’s a fact. 90% of breaches start with human error, often through phishing attacks that trick even the most cautious team members into revealing sensitive data.
Targeted phishing awareness training programs like KnowBe4 or PhishMe simulate real attacks to teach employees how to spot suspicious emails, links, and messages. These platforms track progress with gamified quizzes and customized reports, showing where your team needs improvement. For just $12–$20 per employee annually, you get a solution that pays for itself by preventing costly data leaks.
This isn’t just for big corporations—small businesses and remote teams benefit just as much. Start with a quarterly training session and reinforce lessons with monthly phishing tests to keep security top of mind. 💡
Encrypt All Sensitive Data Transmissions
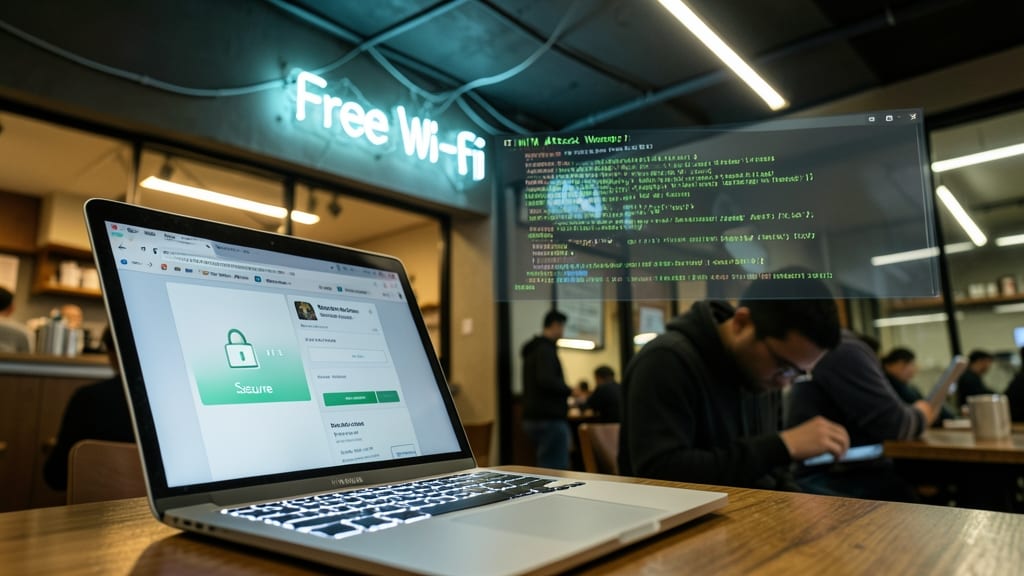
Public Wi-Fi networks and unsecured connections expose your data to man-in-the-middle (MITM) attacks—where hackers intercept sensitive information like login credentials or payment details. Encrypting all transmissions with TLS 1.3 or higher ensures even if data is intercepted, it remains unreadable without the proper decryption key.
Modern browsers automatically enforce encryption for HTTPS sites, but you can take it further with VPNs (like ProtonVPN or NordVPN) or email encryption tools (such as ProtonMail). For businesses, DLP (Data Loss Prevention) solutions add an extra layer by monitoring and encrypting emails, files, and cloud transfers in real time.
Remote workers, freelancers handling client data, and healthcare professionals sharing patient records benefit most from this layer of protection. A few clicks to enable encryption can prevent catastrophic breaches that cost businesses millions annually. ✨
Segment Your Network for Least Privilege
If your business feels like a single, wide-open door for cyber threats, network segmentation is the answer—without requiring a full network overhaul. By dividing your network into isolated zones, you restrict an attacker's ability to move laterally once they breach one area, effectively containing the damage.
Most modern firewalls and routers support VLANs (Virtual LANs) or micro-segmentation, which let you group devices by function—like separating HR systems from guest Wi-Fi. Tools like Cisco Firepower or Palo Alto Networks make this easy to implement with zero-trust principles, ensuring only authorized devices communicate across zones. This approach is especially powerful for businesses handling sensitive data, as it limits exposure without sacrificing productivity.
Perfect for SMBs and enterprises alike, segmentation turns your network into a fortress with checkpoints—not just a single gate. 💪
Monitor with Security Information Events
When your IT team is stretched thin but threats keep coming, a Security Information and Event Management (SIEM) system becomes your digital watchdog. These platforms don’t just collect logs—they correlate security alerts across firewalls, endpoints, and cloud services to spot suspicious patterns before they escalate.
Solutions like Splunk Enterprise Security or IBM QRadar offer real-time threat detection, customizable dashboards, and automated response workflows. For smaller teams, cloud-based options like Microsoft Sentinel integrate with Azure Active Directory and provide AI-driven anomaly detection without heavy infrastructure. The key? Alert correlation that reduces false positives by 70% or more.
This is the tool for organizations that can’t hire full-time security analysts but still need to detect lateral movement or credential abuse. It turns reactive security into a proactive shield. 💻
Prepare for Incident Response Planning
When a breach happens, every minute counts—especially when regulators demand immediate action. Incident response planning isn’t just a checklist; it’s your team’s playbook for cutting containment time by 60% through simulated drills and clear communication protocols.
Start with a predefined escalation matrix that maps roles (e.g., legal, IT, PR) to specific threats, paired with tabletop exercises that test responses to ransomware, data leaks, or DDoS attacks. Tools like NIST’s Cybersecurity Framework or ISO 27035 provide structured templates, while automated incident management platforms (e.g., Splunk ES) streamline real-time coordination.
This isn’t just for enterprises—even small businesses handling customer data (like healthcare or finance) face 72-hour reporting deadlines under laws like GDPR or HIPAA. Practice makes perfect: teams that simulate breaches monthly reduce downtime and fines. 💪